How to Audit a Smart Contract: A Security Playbook
You've been asked to review a Solidity contract before launch. The repository compiles, the unit tests pass, and a static analyzer has produced a reassuringly short report. Then you notice that an administrator can change a critical address, an oracle assumption isn't documented, and one state transition behaves differently when two users interact in sequence. That's the core work of how to audit a smart contract: not just finding familiar code patterns, but proving that the protocol behaves safely when its assumptions are attacked.
A strong auditor moves between source code, system design, economic incentives, tooling, and communication. The same combination also separates candidates who can run scanners from professionals trusted to assess contracts that control user funds.
Why Smart Contract Auditing Matters Now
A contract can execute exactly as written and still cause a severe loss. The failure may sit in the rule itself, in the order of state changes, or in an assumption about users, administrators, tokens, or market conditions. Auditing therefore tests whether the protocol remains safe when those assumptions are deliberately challenged.
The 2016 DAO exploit on Ethereum drained about US$50 million worth of Ether at the time, making review of immutable code a mainstream security requirement rather than an optional practice, as documented in this historical overview of smart contracts. The incident showed how a logic error in deployed blockchain code can become reachable and exploitable without a conventional release cycle.
Immutability changes the review standard
Traditional applications may support emergency patches, rollbacks, feature flags, or server-side intervention. Smart contracts can use upgrade patterns, but upgrades add permissions, administrators, and trust assumptions that must also be reviewed. In a deployment with no upgrade mechanism, a correction can require a new contract and a difficult migration, while users and integrations may continue interacting with the vulnerable instance.
Auditors should prioritize attack surfaces that are expensive or difficult to correct:
- Logic errors: The contract may implement a business rule incorrectly even though each function executes successfully.
- Unsafe state transitions: A sequence of calls may move the system into a state the design never modeled.
- Access-control weaknesses: A missing check, unsafe modifier, or unprotected initialization path can give an attacker control over critical operations.
- External-call assumptions: Tokens, routers, bridges, and oracles may behave differently from the contract's expectations.
A junior reviewer often starts with reentrancy because it is familiar and easy to demonstrate. A senior reviewer traces the attacker's objective, identifies the state variables that govern it, and checks whether the architecture provides a route around the visible safeguards.
Practical rule: Review the contract as a component of a system, not as an isolated file.
The market's scale has also changed expectations for the role. One market study estimated the global smart contract audit market at about US$1.8 billion in 2025, with a projection of US$7.6 billion by 2034 at a 17.3% CAGR, according to Dataintelo's smart contract audit market report. For an aspiring auditor, those figures matter less as a forecast than as evidence of demand for repeatable methods, defensible findings, and clear risk communication.
Hiring managers assess the same capabilities during interviews. They want candidates who can define scope, reconstruct intended behavior, connect a bug to a credible exploit path, and write remediation another engineer can implement. Reviewing blockchain security jobs can clarify how these skills appear in professional roles, but a strong audit demonstrates them through its reasoning, evidence, and prioritization.
The Practical Smart Contract Audit Workflow
An audit can fail before the first command runs. A repository that changes during review can produce findings against code that will never be deployed. Missing architecture notes and trust assumptions create a second risk: reviewers may misunderstand what a function is meant to protect.
Start with a fixed target
Begin with scope and code freeze. Record the exact commit hash, compiler configuration, contracts in scope, deployed addresses where relevant, external dependencies, and explicit exclusions. Ask the team to identify proxy contracts, upgrade administrators, privileged roles, emergency controls, oracles, bridges, and integrations.
The readiness baseline should include architecture documentation, a threat model, functional specifications, and test instructions. A practical smart contract audit checklist emphasizes these inputs because a reviewer needs a stable, reproducible target rather than a moving branch.
Gather evidence before forming conclusions
Read the design documents with the code. Extract the protocol's invariants, user roles, assumptions about tokens and prices, expected failure modes, and rules for deposits, withdrawals, liquidation, rewards, or upgrades. Then build a system map:
- Entry points: List externally callable functions and identify who can call them.
- Assets: Trace where funds, shares, approvals, and accounting values enter and leave.
- State: Record variables governing permissions, balances, lifecycle stages, and limits.
- Dependencies: List each external contract, oracle, router, library, and deployment assumption.
- Trust boundaries: Separate user-controlled data from administrator configuration and external responses.
This map gives automated scans and manual review the same reference point. It also produces the reasoning hiring managers expect in an audit interview: clear scope, explicit assumptions, and a traceable path from behavior to risk.
Layer tools and human review
Run linters and static analysis early. Use project tests, fuzzing, invariant checks, forked simulations, and targeted proof-of-concept tests to challenge adversarial states. Formal verification can help when the team has precise invariants and the logic justifies the effort. It does not replace a threat model or design review.
After automated checks, perform manual analysis, remediation, and fix verification. Guidance on conducting a smart contract audit recommends internal review before an external audit and a post-fix review after remediation. That sequence also matters operationally because audit firms can have 4–6 week queues, while deployment still needs to match the reviewed commit.
Manual and automated review serve different purposes. Automation handles repeatable patterns; auditors interpret business logic, privileged actions, economic assumptions, and interactions across contracts. A guide to source code security auditing provides broader context for structuring that review. In an interview, explain the same trade-off plainly: name what the tools covered, identify what required human judgment, and show why the remaining tests addressed the highest-risk paths.
Before finalizing the report, give every finding an affected location, root cause, exploit scenario, impact, severity rationale, and practical fix. After the team responds, retest the change and confirm that the deployed artifact still matches the audited baseline.
Automated Tools versus Manual Review
The best answer to “Should we use automation or manual review?” is neither. Use automation to increase coverage and speed, then use manual reasoning to investigate what the tools can't understand.
Trail of Bits reported that about 78% of the most severe and easy-to-exploit flaws could probably be detected with automated static or dynamic analysis, while roughly 50% of findings were unlikely to ever be found by automated tools alone, based on its review of audit findings in the Trail of Bits executive summary. The figures overlap because they describe different slices of the findings, not a complete coverage guarantee.
What automation does well
Static analyzers such as Slither can identify suspicious patterns, inheritance issues, visibility problems, and common implementation risks quickly. Symbolic and dynamic approaches, including tools such as Mythril, can explore execution paths and flag conditions that deserve deeper inspection. Fuzzers and invariant testing frameworks push the contract through unexpected inputs and state combinations.
Automation works best when the question is pattern-based or computationally repetitive:
- Known implementation risks: Tools can flag patterns associated with common vulnerability classes.
- Regression detection: A scan can run after each change and identify newly introduced warnings.
- Path exploration: Symbolic or fuzzing tools can exercise states that ordinary unit tests overlook.
- Review prioritization: Findings can direct human attention toward risky functions and dependencies.
The weakness is context. A scanner doesn't know whether an administrator is intentionally trusted, whether an oracle update can distort a liquidation rule, or whether a reward formula remains solvent under a particular sequence of actions unless those properties are modeled explicitly.
What manual review reveals
Manual review tests the protocol's story against its implementation. Read each state transition and ask what happens when calls arrive in an unexpected order, when an external token returns unusual data, when a privileged role is compromised, or when a market assumption fails.
| Audit Method | Strengths | Limitations | Best Use Case |
|---|---|---|---|
| Automated analysis | Fast pattern detection, repeatable scans, useful regression checks | Misses context, economic design flaws, and novel logic paths | Early triage and continuous integration |
| Manual review | Interprets intent, trust boundaries, state machines, and attacker incentives | Slower and dependent on reviewer experience | Critical protocol logic and final risk assessment |
| Hybrid audit | Combines broad automated coverage with contextual analysis | Requires coordination, evidence, and disciplined remediation | Production-bound contracts with complex dependencies |
An interview-ready answer should name this trade-off directly. Don't claim that Slither or Mythril “audits” a protocol by itself. Explain what each tool can surface, what evidence you still need, and how you'll turn a warning into a confirmed exploit or a documented false positive.
Hiring managers also look for the ability to communicate limits without dismissing tools. A candidate who can show a scan, reproduce a finding, write a focused test, and then explain why an economic vulnerability escaped automation demonstrates stronger judgment than someone who merely presents a long output file. Roles such as this smart contract QA engineer opportunity illustrate why testing discipline and security reasoning often overlap.
Vulnerability Categories Every Auditor Must Know
A useful vulnerability taxonomy starts with the attacker's objective, not the name of a famous bug. Ask whether an attacker can steal assets, mint value, bypass a restriction, corrupt accounting, manipulate a market input, or permanently disrupt a critical function. Then trace the code and system conditions that make that outcome possible.
Access control and privileged operations
Access control deserves a full pass, even when the contract uses a recognized framework. Inspect role assignments, role-admin relationships, modifiers, initialization functions, ownership transfers, timelocks, pause controls, upgrade paths, and arbitrary-call capabilities. Confirm not only that a check exists, but that it protects the right operation and cannot be bypassed through an alternate entry point.
The OWASP smart contract security checklists specifically call attention to RBAC, modifiers, initialization, timelocks, and prevention of arbitrary calls. During review, build a privilege matrix that records each role, callable function, state it can change, and recovery path if the role is compromised.
Centralization can also be a design risk rather than a coding error. If one account can change an oracle, replace an implementation, drain a reserve, or alter fees, document that authority clearly and assess whether the protocol's users understand it. A finding may recommend a narrower permission, a delay, a multisignature process, or a transparent governance constraint rather than a simple code edit.
State, external calls, and accounting
Reentrancy is only one form of unsafe interaction. Review the order of state updates and external calls, callback behavior, token hooks, low-level calls, return-value handling, and assumptions about external contracts. Then follow accounting across deposits, withdrawals, transfers, fee collection, liquidation, and emergency paths.
Unsafe state transitions often appear when functions are individually correct but unsafe in sequence. Test repeated calls, partial completion, stale approvals, zero-value inputs, boundary conditions, and interactions between users. Look for inconsistencies between internal balances and actual token balances, especially when the protocol relies on nonstandard token behavior or external settlement.
Economic and governance attacks
The 2025 OWASP Smart Contract Security Top 10 highlights issues such as price oracle manipulation and flash loan attacks, reflecting a shift toward attacks on economic assumptions, as shown in the OWASP 2025 Top 10. A contract can have clean control flow and still fail if it trusts a manipulable price, assumes liquidity that an attacker can temporarily distort, or uses governance powers without adequate delay or separation.
For each oracle, ask who can update it, how freshness is checked, what happens during a stale response, and whether a spot price can be moved within the transaction. For flash-loan exposure, model the attacker's temporary capital, the sequence of swaps or votes available in one transaction, and the invariant that should prevent extraction of value.
A senior auditor turns these categories into evidence:
- Attack vector enumeration: List realistic routes from an untrusted input to an economically harmful outcome.
- Proof of concept: Demonstrate the behavior in a controlled test without overstating impact.
- Triage: Separate exploitable defects from informational concerns and explain the prioritization.
- Remediation report: Give developers a precise fix, affected assumptions, and verification criteria.
Building Your Career as a Smart Contract Auditor
Writing Solidity securely is a foundation, not the finished role. An auditor must read unfamiliar code quickly, reconstruct a protocol's economic model, identify attacker-controlled paths, and communicate risk to people who may not share the same technical vocabulary.
Interviewers often test that transition through practical scenarios. They may ask you to review a withdrawal function, explain a privilege-escalation path, design a proof of concept, or rank several findings by exploitability and impact. The strongest response begins by clarifying assumptions, identifies the relevant state and trust boundaries, and explains what evidence would confirm or reject the hypothesis.
Build a portfolio that shows judgment
A useful portfolio doesn't need to be a collection of polished claims. It should show your reasoning:
- Write mini-audits: Choose small open-source contracts and document scope, assumptions, findings, severity, and remediation.
- Reproduce known exploits: Use isolated test environments to understand how the vulnerable state becomes reachable.
- Publish tool-assisted work: Include Slither output or fuzzing results, but explain which warnings mattered and which did not.
- Practice reporting: Write concise findings that a protocol engineer can implement without a follow-up meeting.
- Review design, not only code: Document oracle, governance, upgrade, dependency, and operational assumptions.
Interview guidance for smart contract auditors emphasizes Solidity knowledge, common vulnerabilities, attack-vector enumeration, proof-of-concept exploits, triage, and clear explanations, as outlined in this smart contract auditor interview guide. That combination is important. A candidate who spots a bug but cannot explain its exploitability or remediation may not be ready to own an audit finding.
Progress from operator to security engineer
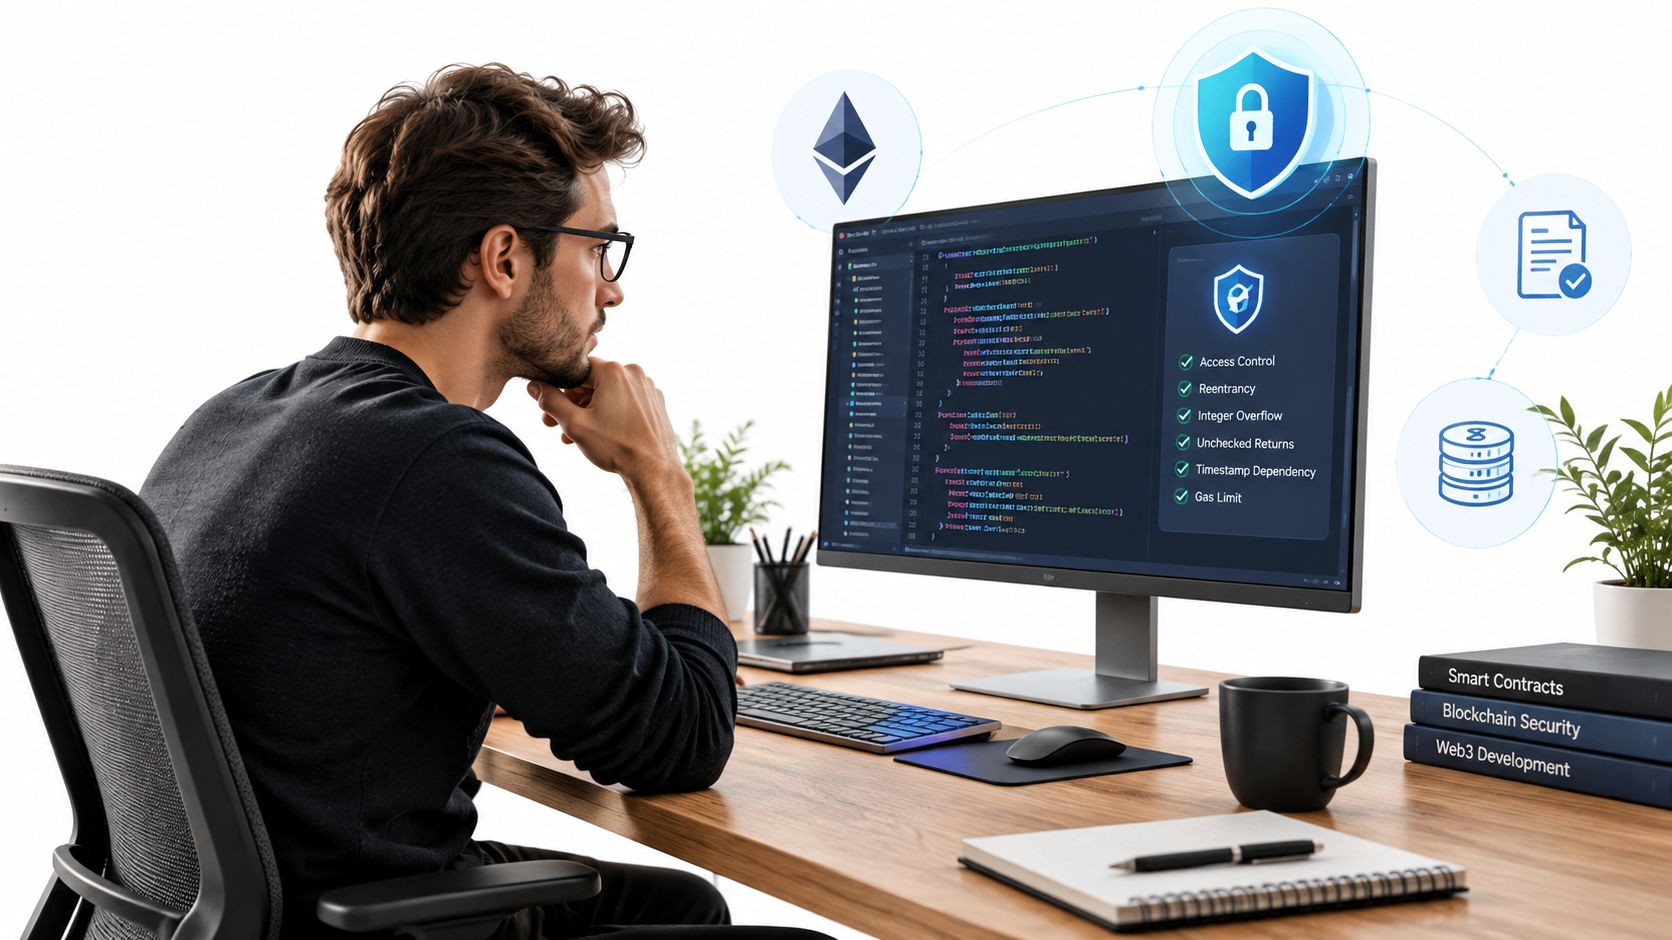
At an entry level, become reliable with repository setup, Solidity semantics, testing, static analysis, and common vulnerability patterns. The next step is learning to model state machines, external dependencies, and economic incentives. Senior work adds scope control, review leadership, finding triage, client communication, remediation verification, and the ability to recognize when a design cannot be made safe with a local patch.
Agentic and AI-assisted auditing add another layer of judgment. A 2025 technical report on agentic smart-contract auditing discusses persistent false negatives, false positives, and incomplete coverage when invariants or external context are missing. Treat these systems as assistants for exploration and prioritization, not as substitutes for a reviewer who understands the protocol and verifies the final result.
The surrounding system also belongs in your professional scope. Review CI/CD controls, dependency management, deployment procedures, signing and key infrastructure, monitoring, emergency response, and changes made after the audit. A secure contract can still be deployed incorrectly or operated through a compromised privileged workflow.
A practical career test is simple: can you explain not only what is wrong, but how an attacker reaches it, what the impact is, how confident you are, what should change, and how you'll verify the fix? If you can do that consistently, your audit methodology is becoming professional competency rather than tool familiarity. For senior opportunities, review roles such as this senior smart contract auditor position and compare the expectations with the evidence in your portfolio.
Blockchain Jobs helps you find specialized Web3 roles across security, engineering, quality assurance, and related disciplines, including opportunities where smart contract auditing and protocol risk skills matter. Visit Blockchain Jobs to explore current openings, compare career paths, and turn your audit practice into your next blockchain opportunity.